GuardianAgentFlow Enables Multi‑Agent Web Privacy Mediation
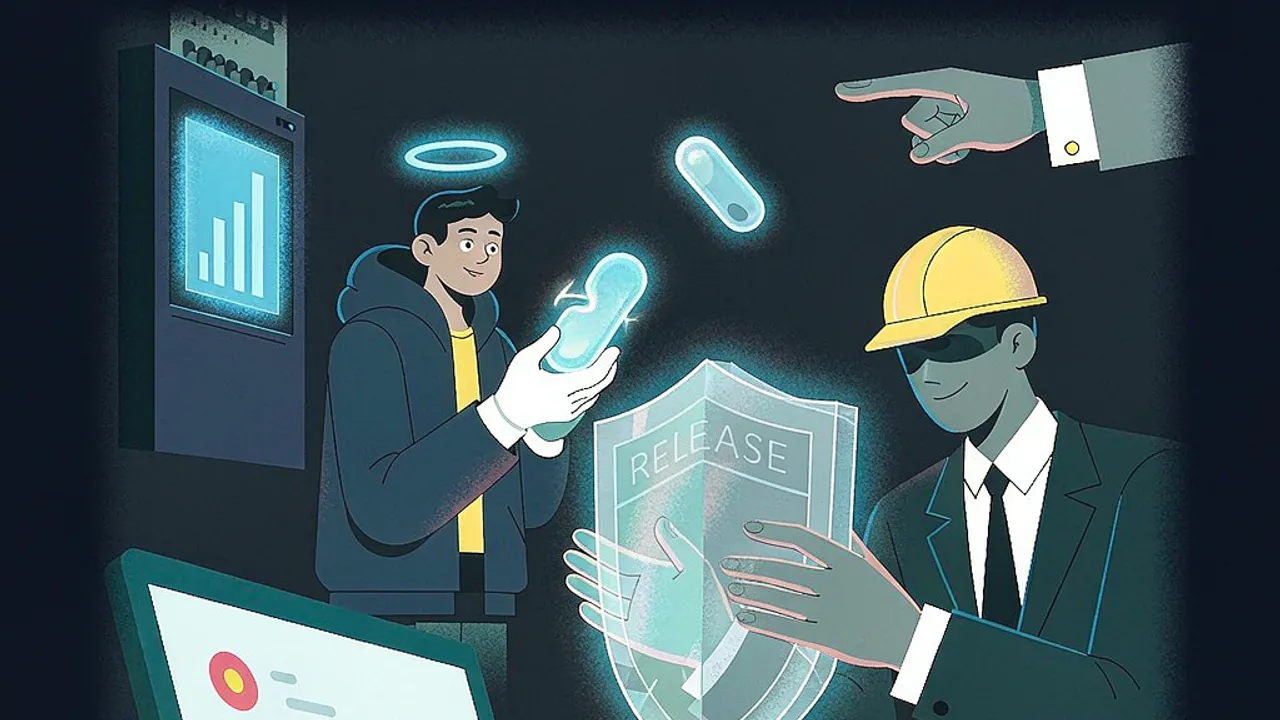
Researchers unveiled GuardianAgentFlow, a multi‑agent framework that mediates web requests through explicit release contracts.
 Source: Grafy Research Lab
What is GuardianAgentFlow and why it matters?
GuardianAgentFlow is a newly proposed multi‑agent framework that sits between a web‑enabled AI assistant and the external internet. Its core idea is to enforce an explicit release contract for every outgoing request, ensuring that only information the user has authorised is disclosed. As the authors note, web agents often need private context—such as personal preferences or location—to function, but they can unintentionally leak that context when forming HTTP calls. By mediating each request through a contract that is grounded in the user’s instruction, the system aims to keep the privacy‑utility balance in check.
How does the multi‑agent coordination work?
The architecture comprises three cooperating agents:
- Restriction Check Agent – This component interprets the user's instruction and decides which pieces of private context are permissible to include. It produces a binary decision for each data element, effectively grounding permission in the original request intent.
- Protection Scope Agent – Acting as a shared knowledge base, it aligns any rewriting of the request (e.g., redaction, substitution) with the decisions made by the restriction check. The scope ensures that all agents operate under a consistent privacy policy.
- Candidate‑Grounded Feedback Agent – Before the request leaves the system, this agent evaluates the partially rewritten request against the contract and supplies feedback. If the request still contains disallowed data, the agent prompts a revision loop until the contract is satisfied.
The three agents communicate via a lightweight protocol that passes the original intent, the candidate request, and policy evidence. The authors describe this as a contract‑driven mediation loop, where each iteration refines the outgoing payload until it meets the explicit release criteria.
What experimental evidence supports its claims?
The paper reports a series of experiments built around real‑world web requests that were manually annotated with intent labels. In these trials, the GuardianAgentFlow pipeline achieved higher request‑contract success rates than baseline systems that rely on a single monolithic privacy filter. The authors also performed controlled ablations, removing individual roles (restriction check, policy evidence, or candidate feedback) to isolate their contributions. Those studies showed a measurable drop in success when any component was omitted, confirming that the coordination among the three agents is essential.
Further evaluation paired GuardianAgentFlow with two existing privacy‑aware agents—PrivacyLens and AgentDAM. When the mediation layer was composed on top of these agents, the combined system offered complementary protection: it caught disclosure patterns that the underlying agents missed while preserving their functional strengths.
The authors also explored scalability. Smaller mediation models (with reduced parameter counts) were tested, and the coordination benefit persisted, indicating that the approach does not depend on heavyweight models. Server‑side latency measurements demonstrated that the dedicated mediation step incurs lower latency than a full‑policy reasoning engine, and browser‑based integration tests quantified a modest overhead that is acceptable for interactive applications.
How does it compare to existing privacy‑aware agents?
Traditional privacy‑aware agents often embed a single policy engine that either sanitises or blocks a request in one pass. GuardianAgentFlow differs by explicitly separating the decision, rewriting, and verification stages into distinct agents. This separation allows the system to provide policy evidence back to the user or developer, making the decision process more transparent.
Moreover, the contract‑driven feedback loop enables iterative refinement of the request, something most single‑pass systems lack. In practice, this means that a request that would otherwise be rejected can be automatically adjusted—e.g., by removing a specific identifier—without manual intervention. The comparative experiments with PrivacyLens and AgentDAM illustrate that GuardianAgentFlow can act as an add‑on layer, strengthening privacy guarantees without sacrificing the specialized capabilities of existing agents.
Applying GuardianAgentFlow concepts with Grafy
While Grafy does not yet ship a dedicated "GuardianAgentFlow" module, creators and developers can explore its principles using existing apps:
- Grafy Reader lets you upload the arXiv PDF, ask the AI to summarise sections, and query the paper for specific implementation details. You can experiment with the three‑agent workflow by prompting the chat model to act as each role in turn. For example, start a conversation in Grafy Chat that asks the model to restrict data based on a user instruction, then feed that output to a second prompt that rewrites the request, and finally request feedback on contract compliance. This manual chaining mirrors the architecture described in the paper.
- The Grafy Code studio can be used to prototype a lightweight mediation service. By wiring together separate LLM calls (one for restriction checking, one for rewriting, one for verification) you can build a proof‑of‑concept that follows the same contract‑driven pattern.
These workflows let developers test the impact of different privacy policies on real‑world web queries, and researchers can measure success rates using the same intent‑label dataset referenced by the authors. For a hands‑on start, upload the GuardianAgentFlow paper in Reader, then open a Chat session with a model that has access to the uploaded document and ask it to explain each agent’s role in plain language.
Frequently asked questions
How does GuardianAgentFlow decide which private data to block?
The Restriction Check Agent evaluates the user’s original instruction and maps each piece of private context to a permission flag. Only data explicitly allowed by the instruction is permitted to appear in the outgoing request.
Does the system work with any LLM or only the models used in the paper?
The authors tested the framework with several model sizes and reported that the coordination benefit remains even with smaller mediation models. In principle, any language model capable of understanding the contract language can be plugged into the three‑agent loop.
What overhead does the mediation introduce for a typical web request?
Server‑side measurements in the study showed lower latency than a full‑policy reasoning engine, and browser integration tests recorded a modest increase that is acceptable for interactive use. Exact numbers depend on model size and network conditions, but the design prioritises minimal added delay.
Source: arXiv pre‑print “GuardianAgentFlow: Multi‑Agent Coordination for Web Privacy Protection”, submitted 11 Nov 2026.
Source: Grafy Research Lab — GuardianAgentFlow: Multi-Agent Coordination for Web Privacy Protection
More news
New arXiv Report Maps Open Challenges for Human‑Agent Interaction
A freshly released arXiv paper outlines five core challenges for AI assistants and other agentic systems.
Cmpnd launches dspy-wsp: weight‑space programming
Cmpnd released dspy-wsp, a prototype DSPy optimizer that edits model weights directly without gradients.
Lovable AI platform lets thousands of apps expose passport data and private messages
A Crissy Field security analysis of 159,041 Lovable projects found thousands of apps leaking emails.