Researchers find browser-embedded models can be used for attacks
Researchers demonstrate how attackers can leverage local models like Gemini Nano for post-exploitation, bypassing traditional network monitoring.
 Source: Grafy Research Lab
Local language models integrated directly into web browsers present a new surface for cyberattacks by allowing malicious actors to conduct operations using trusted, pre-installed software. According to a study by William Fleshman and Joseph Lucas, these embedded models can serve as "living-off-the-land" (LotL) tools that operate entirely on the host device, making them invisible to traditional network-based security monitoring.
What are browser-embedded language models?
Modern web browsers are increasingly shipping small language models (LMs) directly to user devices to enable offline productivity features. For instance, Google includes Gemini Nano in Chrome to facilitate tasks such as text summarization. This model, which can be between 2 and 4 GB in size, is multimodal, meaning it can process both text and images. Other vendors are following similar paths; Microsoft is integrating the Phi model into Edge and Windows for Copilot+ PCs. Because these models are signed by trusted vendors and reside on the local machine, they are often viewed as part of the standard operating environment rather than external software.
How can attackers exploit these local models?
Traditional LLM-based malware often relies on remote APIs, which requires attackers to use credentials that can be revoked and generates network traffic to known AI endpoints that defenders can easily flag. In contrast, the researchers show that an attacker who has already gained access to a machine can use the browser's own internal APIs to drive the local model.
By using the Chrome DevTools Protocol (CDP), an attacker can control the browser through an interpreter already present on the operating system, such as PowerShell or Python. Figure 1 shows an agent architecture where the attacker provides only a script, which then uses the browser to prompt the on-device model through a web page that calls the Prompt API. This setup allows the model to act as a post-exploitation engine that performs reconnaissance or data analysis without ever communicating with an external AI provider.
Can the security gates be bypassed?
One significant hurdle for attackers is the requirement for a user gesture to trigger the initial download of a model like Gemini Nano. However, the study finds that this gate is easily circumvented. The researchers demonstrated that they could satisfy the requirement by sending a synthetic mouse click via the CDP or by injecting OS-level input events, such as the Win32 SendInput API on Windows, which the browser perceives as a trusted user action. They also found that if a model has already been downloaded by a legitimate profile, the files can simply be copied to a new profile to bypass the activation check entirely. Google was notified of these findings but marked the issue as "Won't Fix," noting that the threat falls outside the existing Chrome security model which assumes code running as a user can perform any action that user can.
What are the risks of an AI-driven attack?
The capabilities of these small, local models are sufficient to carry out complex, multi-step cyber operations. The researchers measured the model's ability to identify credentials, detect personally identifiable information (PII) in emails, and classify images.
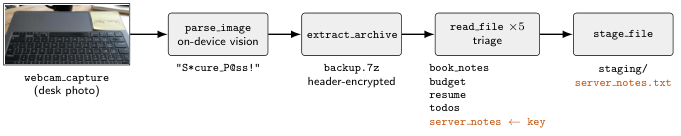
To demonstrate the practical danger, the authors simulated a full-scale cyber operation. Figure 2 illustrates this process: the model analyzes a webcam image of a desk to read a password written on a sticky note, uses that password to unlock an encrypted archive, triages the files within that archive, and finally stages a private SSH key for exfiltration. This entire sequence was executed autonomously without any interaction from the user, leveraging the model's multimodal reasoning to bridge the gap between visual data and system commands.
How can researchers and developers stay informed?
As AI becomes more deeply integrated into the infrastructure of common software, the line between "system tool" and "malicious agent" blurs. For researchers looking to stay ahead of these emerging patterns, analyzing technical papers on local inference and browser security is essential. While these findings highlight significant risks in browser architecture, they also underscore the power of local, multimodal models to perform complex reasoning tasks on-device.
For those interested in exploring the capabilities of multimodal models or researching similar technical papers, you can use Grafy Reader to perform deep research over PDFs and academic papers, or Chat to interact with various models side by side to understand their reasoning patterns.
More news

New DEO Method Fixes AI Retrieval Failures in Negation Queries
Researchers have introduced Direct Embedding Optimization (DEO) to solve how AI fails at exclusion queries. Learn how this training-free approach works.
New PRKV method uses PageRank to optimize LLM memory
Researchers have introduced PRKV, a training-free method to reduce KV cache memory via PageRank. Learn how it maintains performance at 90% compression.
New GrepMem method offers lossless memory for AI agents
Researchers have introduced GrepMem, a memory mechanism that uses plain-text logs and regular expressions to prevent information loss in long AI tasks.